What it does
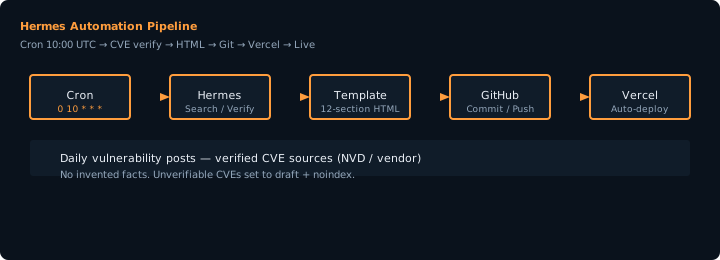
Every day at 10:00 UTC, a cron job (0 10 * * *) runs the homelab-vulnerability-post skill. It searches the web for new CVEs affecting homelab stacks (Proxmox, Docker, LXC, Jellyfin, TrueNAS, Audiobookshelf), verifies with vendor / OpenCVE / NVD / CISA sources, writes a structured HTML entry using the documented 12-section template, commits, pushes to github.com/kiraitachi/Ciberdefensa.uk, and Vercel deploys it automatically to ciberdefensa.uk.
How Hermes connects
The agent runs locally on the Linux host. It reads the skill instructions, executes the web-search / verify / write steps, and pushes via a configured remote URL with the GitHub PAT stored as an environment variable (fine-grained GitHub token limited to this repository). The site is hosted on Vercel, which builds from the main branch — so every push is live within seconds.
Structure enforced
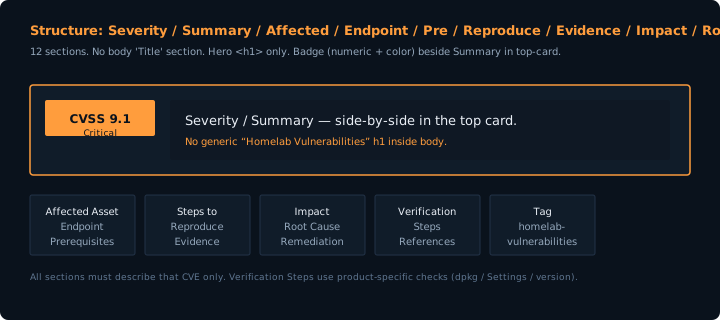
New entries always use the redesigned format validated on CVE-2024-21626: Severity badge (numeric CVSS, color-coded) + Summary card side-by-side, followed by section cards for Affected Asset, Endpoint, Prerequisites, Steps, Evidence, Impact, Root Cause, Remediation, Verification Steps, and References. No generic "Homelab Vulnerabilities" <h1> inside the post — that label belongs only to the index filter.
Current pipeline
- Cron:
0 10 * * *(scheduled daily at 10am UTC) - Skill:
homelab-vulnerability-post(structured rules + visual design) - Source repo: github.com/kiraitachi/Ciberdefensa.uk
- Deploy target: Vercel (auto-build from
main) - Live site: ciberdefensa.uk
What is still work-in-progress
This entry itself is a WIP note — changes and updates to the automation are tracked on GitHub, not rewritten into each blog post. The daily feed is operational; the visual redesign (badge + card layout) has been applied to all existing vulnerability entries.